
GitHub MCP Claude Code: Setup & Security Guide
Connect Claude Code to GitHub MCP, inspect a scoped repository at an exact revision, and review write actions before execution.
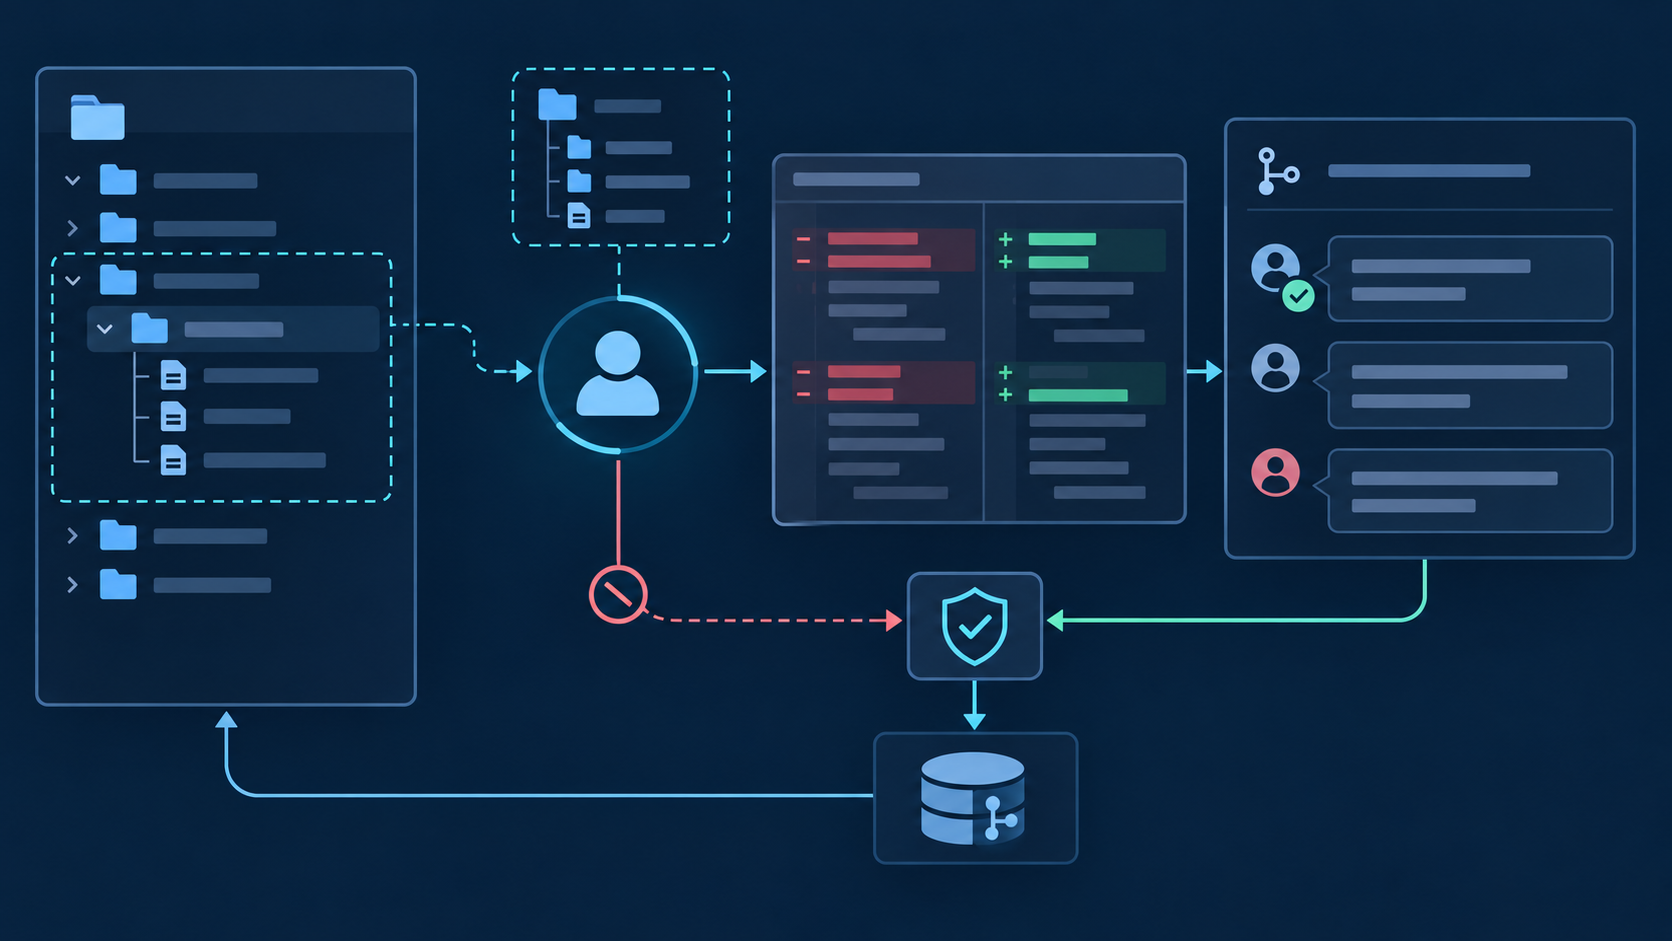
What GitHub MCP adds to Claude Code
Claude Code already understands a local working tree. GitHub MCP adds server-side collaboration context: repositories, branches, commits, issues, pull requests, review threads, checks, releases, and other capabilities exposed by the selected toolsets. That distinction matters. Local Git answers “what is on this machine?” GitHub answers “what is published, reviewed, discussed, or running remotely?” A reliable workflow states which source is authoritative for each decision and records the exact repository and revision used.
Begin with repository metadata, a known file, issue, or pull request. Confirm identity and scope before exposing any mutation tool.
Branch names move. Retain the commit SHA or pull-request head SHA that supported the analysis so another reviewer can reproduce it.
Local edits, GitHub comments, branches, reviews, and merges have different consequences. Do not treat them as one generic “write” action.
Before a remote write, show the target, exact payload, expected result, checks, and rollback path. Approval should cover a concrete action.
Choose the official connection and credential model
GitHub maintains the official GitHub MCP Server and documents both a GitHub-hosted remote server and a local container. The remote route is simplest when the MCP client and organization policy support it. The local route is useful when your environment requires explicit container execution or a personal access token. In either case, the credential—not the prompt—determines which private resources and actions are possible.
| Decision | Hosted remote | Local container | Review point |
|---|---|---|---|
| Operation | GitHub runs the server; Claude Code connects over supported remote transport. | Claude Code starts the official container through STDIO. | Client compatibility, network policy, container policy. |
| Authentication | Use the authentication flow supported by the hosted integration. | Pass a narrowly scoped GitHub token through the environment. | Identity, repository grants, expiry, rotation. |
| Updates | GitHub manages the hosted service. | Your environment selects and updates the container image. | Change review, image provenance, rollback. |
| Scope | Controlled by account, organization policy, and exposed toolsets. | Controlled by token permissions, environment, and server options. | Read versus write, named repositories, tool allowlist. |
List the owner and repository names required for the task. Decide whether forks, private repositories, organization projects, and user-level resources are needed. A vague “all GitHub” scope is not a setup requirement.
The official server groups capabilities by domain. Enable the smallest set that supports the workflow—for example repository reading and pull requests—rather than exposing every available tool by default.
For a local server, keep the token in the environment or an approved secret manager. Never paste a live credential into MCP JSON that will be committed, a prompt transcript, an issue, or a shell-history example.
Follow the current command in the official server documentation for the chosen transport. Then use Claude Code's MCP view to confirm the server is connected and review the actual tools it exposes.
Read one public or approved private file at a named branch and compare its path and content with GitHub. Next retrieve one issue or pull request and confirm number, state, author, and URL.
A reviewable GitHub workflow for Claude Code
A good request names four things: the repository, base revision, collaboration object, and deliverable. For example: inspect pull request 214 in owner/repo against its base SHA, compare unresolved review threads with the current diff, and return findings without posting comments. This is far safer and more reproducible than “review our latest PR.”
| Stage | Claude Code should do | Evidence to retain | Approval gate |
|---|---|---|---|
| Orient | Resolve repository, default branch, PR head/base, issue state, and local remote. | Owner/repo, URLs, branch names, SHAs. | No remote write. |
| Investigate | Read files, commits, checks, reviews, linked issues, and relevant history. | Exact paths, lines, check names, timestamps. | No mutation tool. |
| Plan | Explain findings, proposed local changes, tests, and remote actions separately. | Risk, assumptions, affected files, expected outcome. | Approve implementation scope. |
| Validate | Apply local patch, run relevant checks, inspect diff, and re-read changed GitHub state. | Test output, diff summary, remaining failures. | Approve exact remote payload. |
| Publish | Perform only the approved comment, branch, PR, review, label, or merge action. | Result URL, new SHA or object ID, final state. | Stop after confirmed result. |
Useful review prompt: “Read pull request 214 in owner/repo and its unresolved review threads. Compare the head SHA with the base SHA and inspect relevant local files. Return only evidence-backed findings with file paths and lines. Do not post, approve, request changes, merge, label, or modify the repository.”
Control risk at credential, tool, and action layers
A prompt saying “read only” is useful behavior guidance, but it is not an authorization boundary. Enforce least privilege in GitHub credentials and organization policy, reduce the MCP toolset, and require human confirmation for consequential calls. Also remember that read access is sensitive: source code, issue bodies, private review comments, Actions logs, and release artifacts may contain internal or regulated information.
Prefer fine-grained, expiring credentials or managed authorization with named repository grants. Rotate after suspected exposure and remove access when the workflow ends.
Expose read toolsets by default. Add issue, PR, release, workflow, or administration mutations only when the active task requires them.
Show the exact comment, title, body, branch, label, review state, or merge target before calling the write tool. Do not approve a placeholder.
Record the operator, time, repository, revision, tool, parameters, outcome, and resulting GitHub URL. Logs should support reconstruction without storing secrets.
Common failure modes
- Repository not found: distinguish a wrong owner/name from a private repository hidden by the credential. Test identity and a known accessible repository.
- Local and remote disagree: compare remotes, forks, branches, commit SHAs, shallow history, and unpushed commits before deciding either side is stale.
- PR data looks incomplete: check pagination, review-thread resolution, renamed files, generated files, and whether the tool returned the current head SHA.
- Action is forbidden: inspect token permissions, branch protection, rulesets, required reviews, organization policy, and toolset configuration. Do not broaden access blindly.
Use QVeris for capabilities outside GitHub
GitHub MCP should remain the direct source for GitHub repository and collaboration state. A live QVeris catalog search did not surface a trustworthy exact GitHub Tool or Provider profile—the guessed routes resolved to unrelated content—so this page does not use them. When the same Claude Code task needs other APIs or live data, consult QVeris Docs and evaluate the required capability in the QVeris Playground.
- Keep GitHub as the provenance source for code collaboration objects.
- Validate any additional QVeris capability independently before composing it with GitHub writes.
- Preserve separate approvals and audit records for repository operations and outside-system actions.
GitHub MCP for Claude Code FAQ
No. Local Git manages the working tree and local history; GitHub MCP exposes hosted collaboration state and permitted remote actions. Many workflows need both.
Use GitHub's hosted server when client support and policy allow it. Choose the official local container when you need explicit runtime and token control.
Start with read-only toolsets and credentials. Add only the mutation needed for an approved task, then verify the exact payload before execution.
You may be looking at different forks, remotes, branches, or SHAs, or have unpushed local commits. Compare immutable revisions instead of branch names alone.
Yes. Ask it to inspect the base/head diff, checks, review threads, and relevant files, then return evidence-backed findings without posting until approved.
Pass secrets through approved environment or secret-management mechanisms, exclude local configuration where appropriate, and scan staged changes before committing.
References and next steps
GitHub MCP Server
GitHub MCP security guidance
GitHub token guidance
GitHub repository rulesets
Claude Code MCP documentation
QVeris Docs
QVeris Playground